The Binary Protocol: How HSTS Supercookies Weaponize Secure Routing
The Subversion of Transport Security
The padlock in your address bar is supposed to be one of the good guys. Security advice has hammered the same point for years: check for it, trust it, never send anything sensitive without it. Behind that little icon sits a protocol called HTTP Strict Transport Security, or HSTS, and its job is genuinely protective. When a website issues an HSTS instruction, it tells your browser to refuse any unencrypted connection to that site, ever — slamming the door on downgrade attacks that try to strip your traffic back to plain text.
There's a catch hiding in how well it works. For the rule to stay effective, your browser has to remember it, permanently, with no expiration. And anything a browser remembers permanently is something a tracking network can write to.
That's the pivot data brokers exploited. They aren't breaking HSTS or weakening your encryption. They're using its memory as a place to store a number — one that clings to the security layer of your browser rather than to any deletable file. Clear your cache, wipe your cookies, switch to an incognito window, and the number is still there, because none of those actions touch the transport-security rules your browser is dutifully keeping safe.
How Encrypted Routing Redirections Create a Binary Identity
Start with what an HSTS supercookie is not: it is not a file sitting on your hard drive. There's nothing in a folder to find. What it actually is is a configuration — a particular pattern of which sites your browser has been told to always load securely and which it hasn't. Read that pattern the right way, and it spells out a number.
The setup happens in a burst of background requests you never notice. Land on a platform a tracking network controls, and your browser is quietly told to load dozens of invisible tracking pixels, each one hosted on its own unique subdomain. That fan-out of subdomains is the scaffolding the whole scheme is built on.
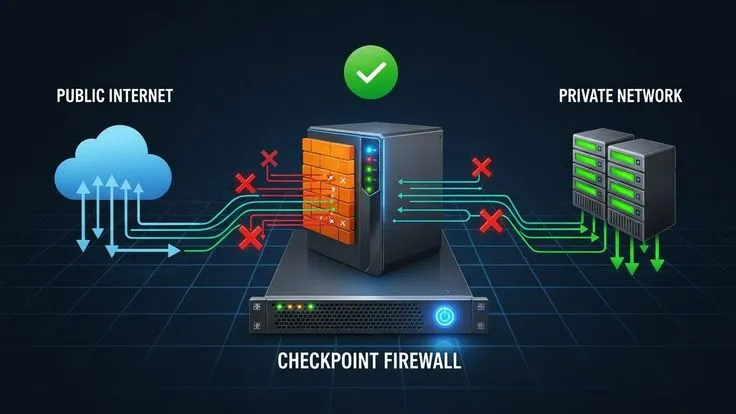
Then the server makes its assignments. For some of those subdomains it issues an HSTS command, locking them to encrypted-only connections. For others it deliberately does nothing, leaving them unsecured. Picture the result as a row of switches: a secured subdomain is a one, an unsecured one is a zero. Across all those pixels, your browser ends up holding a specific binary string — a tracking number etched into its routing rules without a single consent prompt.
"This isn't just advertising; it's the subversion of the very protocols meant to keep us safe. We're seeing security features being exploited to create tracking identities that users can't easily see or delete."
— Lead Cybersecurity Researcher
The reconstruction is where it turns genuinely persistent. Visit an affiliated site later and it requests those very same pixels, this time over plain unsecured connections. Here your browser betrays the pattern automatically: for every subdomain it was told to secure, it silently upgrades the request to encryption; for the rest, it leaves the request alone. The server simply watches which pixels arrive over a secure channel and which don't. Secure means one. Unsecured means zero. In an instant, your exact binary identity is rebuilt — and it was your browser's own protective behavior that read it back out.
This is the uncomfortable irony of the technique. Obeying strict transport security is precisely what keeps you safe from network tampering, so your browser does it faithfully every time. Standard privacy extensions and cookie blockers watch for stored data and known tracker scripts; they have no concept of a fingerprint written in routing decisions, which is why they stare straight past it.
Technical Strategies for Network Protocol Defense
The reflex to "clear everything" fails here for a reason worth understanding. There's no stored payload to purge — the identity lives in protocol rules, and a data wipe leaves it perfectly intact. Defending against this calls for a different instinct entirely: stop the pattern from ever being written, rather than trying to erase it afterward.
The whole scheme depends on one fragile precondition — your browser has to be marched through a tightly coordinated matrix of unique subdomain requests. Break that, and there's nothing left to assign. The practical way to break it is connection containment: cutting off contact with the unverified tracking networks that host these redirection matrices before the sequence can even begin. Advanced content filtering can recognize the structural broker nodes behind the scheme and block them at the source, so the initialization requests never fire. With no contact, your browser is never handed its row of switches to flip, and the binary string is never created.
There's a quieter discipline that reinforces all of this. Every active background script you tolerate is one more opening for systemic protocol manipulation, so trimming that footprint shrinks the surface any supercookie attempt has to exploit. The throughline stays consistent: deny the coordinated requests up front, because once the routing rules are set, the number has already been written.
Securing Your Network Protocol with the Total Adblock Browser Extension
Spotting a fan-out of tracking subdomains and severing it before the HSTS assignments land isn't something anyone can realistically do by hand. The Total Adblock browser extension handles that interception automatically. Supercookies abuse the native security infrastructure your browser is right to maintain, but the script commands that kick the process off — and the external databases that store your binary identity — originate from unverified third-party marketing exchanges. That outside dependency is the seam where the technique can be cut.
The Total Adblock browser extension analyzes structural web code and severs outbound connections to known data brokers, malicious tracking platforms, and invasive advertising networks before they can deploy their tracking matrices. When the initiating connection never completes, the subdomain sequence never runs, and there's no pattern of secured and unsecured routing rules for a server to read back. What you're left with is a faster, cleaner, more orderly browsing experience. And if you spend time streaming, it also removes in-play video ads so playback runs without interruption.
It asks little of you in exchange, running quietly in the background with no complex technical setup to wrestle with. Through intuitive presets, Total Adblock offers tailored filtering you can shape around your own priorities — leaning toward advanced privacy or stricter system security, whichever fits how you browse. You keep full authority over your own list of trusted websites and acceptable connections, so the sites you genuinely rely on keep working as they should. Put the extension to work, and you stop external servers from using hidden routing architecture to compromise your digital identity.
The padlock was meant to protect you, not to label you. Keeping its memory out of a broker's reach is what keeps it doing only the job it was built for.
Precision Protection
Connection Containment
Total Adblock analyzes outgoing web traffic and intercepts connections to known tracking platforms before they can deploy complex routing scripts.
HSTS Defense
Prevents tracking platforms from writing persistent binary signatures to your browser's protocol storage, preserving your digital privacy.
Ad-Free Browsing
Clears intrusive video ads and pop-ups automatically, delivering a cleaner, faster, and more streamlined browsing experience.
Three Steps to Total Security
Get the App
Click any "Get the App" button on this page to visit the download center.
Add to Browser
Install the lightweight extension with a single click in your browser's store.
Enable Protection
Open the extension and toggle the main switch to secure your network protocol instantly.
Frequently Asked Questions
How do HSTS supercookies track my browsing? expand_more
HSTS supercookies exploit your browser's built-in secure connection memory. By directing your browser through a specific sequence of encrypted and unencrypted subdomains, tracking networks can write and read a unique binary code without placing any files on your device.
How does Total Adblock prevent HSTS supercookies? expand_more
Instead of trying to clear the HSTS cache—which browsers restrict—Total Adblock blocks the connection to known tracking subdomains before the sequence can start. This prevents the binary signature from ever being written.
Will this affect my access to secure websites? expand_more
No. Total Adblock only blocks known tracking matrices and advertisement networks. Your access to legitimate, secure websites using standard encryption (HTTPS) remains completely unaffected.
Ready to Reclaim Your Digital Sovereignty?
Block the Binary Protocol. Stop persistent tracking. Experience the web as it was intended.
Try Total Adblock today and browse securely.
Disclaimer: This page is a paid advertorial brought to you by gydespot.com. It is intended for promotional purposes only and should not be considered independent journalism, editorial content, or consumer advice. The content has been created or curated by the advertiser and may include affiliate links. We may receive compensation if you choose to purchase a featured product or service via the links provided. Please refer to our Advertising Disclaimer and Privacy Policy for more information.